Crypto scammers who stole thousands and thousands from Russian-speaking traders approached the identical victims weeks later, promising to get well their losses.
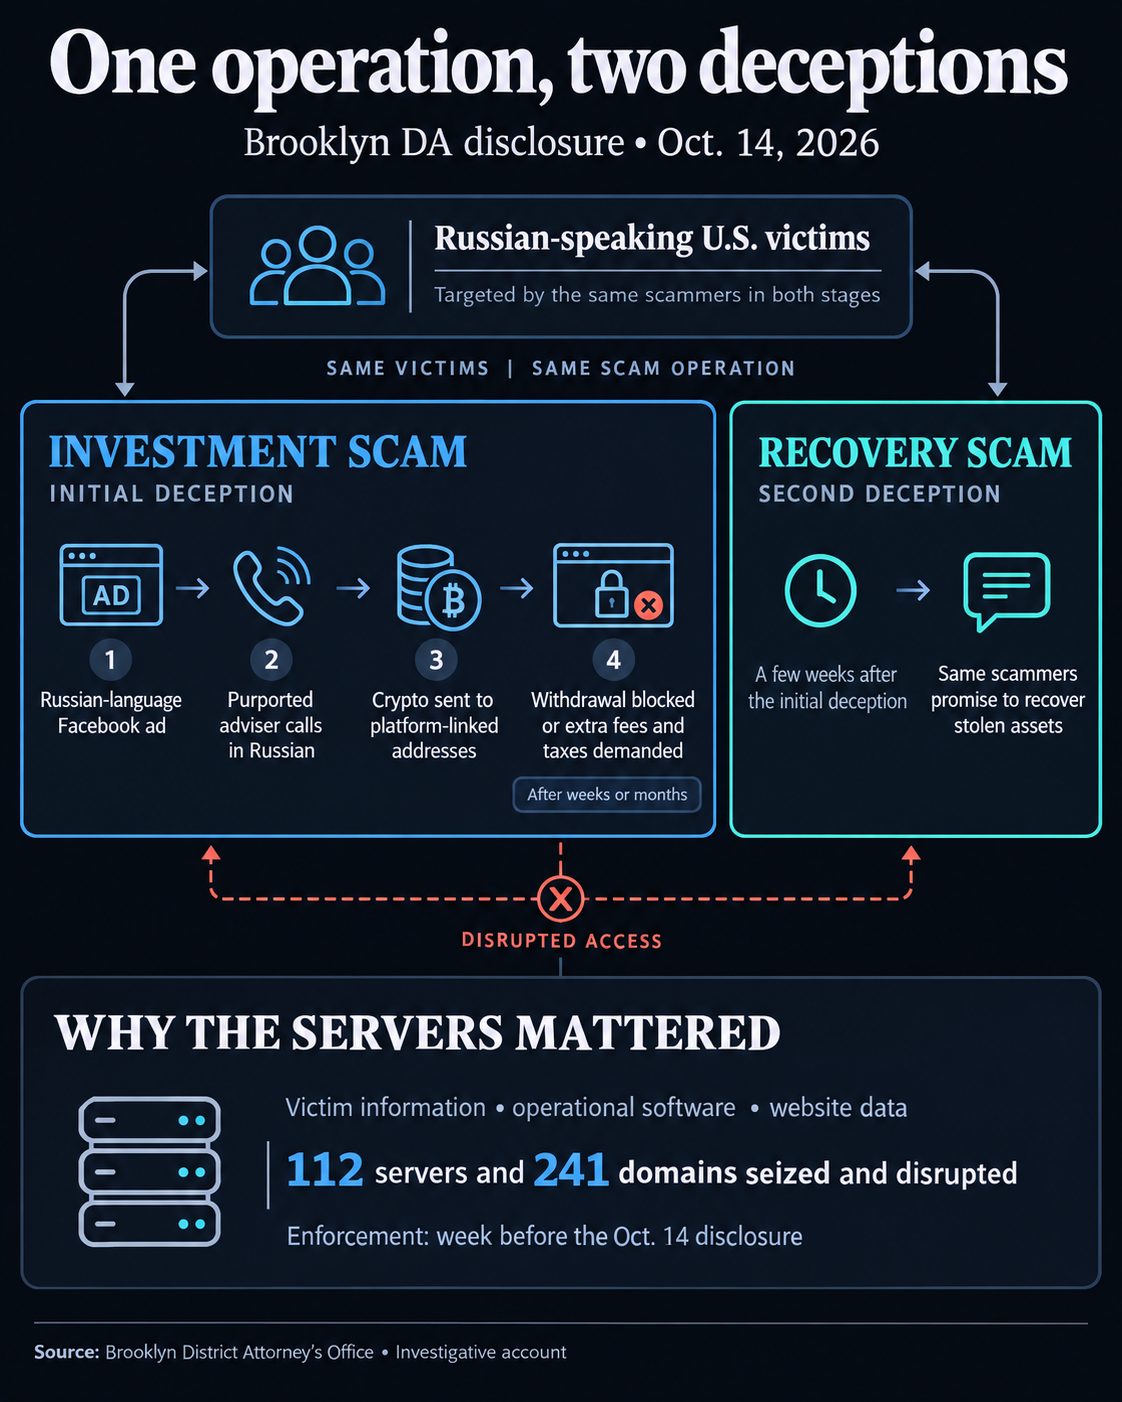
On Oct. 14, Brooklyn prosecutors disclosed the fraud after a global enforcement operation disrupted 112 servers and 241 web sites supporting a cryptocurrency funding scheme that allegedly stole tens of thousands and thousands of {dollars} from victims throughout the USA.
The operation, carried out with assist from the Federal Bureau of Investigation (FBI), focused the infrastructure used to run fraudulent funding platforms and preserve involved with victims. Investigators recovered information exhibiting the identical prison community tried to use individuals once more after they misplaced cash within the unique scheme.
Brooklyn District Legal professional Eric Gonzalez stated the scammers had focused Russian-speaking Individuals by an elaborate funding operation earlier than trying to extract additional funds by providing to retrieve stolen cryptocurrency.
The investigation, which has been underway for 3 years, recognized a focus of victims in Brooklyn, dwelling to a big Russian-speaking inhabitants. Some victims misplaced their total life financial savings, in keeping with prosecutors.
The recovered data additionally uncovered how the fraudsters maintained relationships with victims past the preliminary theft, creating alternatives to solicit extra funds after their fraudulent funding platforms stopped processing withdrawals.
Prosecutors goal servers behind repeat crypto rip-off
Investigators traced the operation to Russian-language Fb adverts selling cryptocurrency funding alternatives.
Individuals who responded to the adverts acquired cellphone calls from people posing as Russian-speaking funding advisers. The purported advisers then directed them to cryptocurrency buying and selling web sites, helped them create accounts, and instructed them to buy digital belongings.
Victims subsequently transferred cryptocurrency to pockets addresses linked to the funding platforms, believing their cash was being deployed in official investments.
The deception sometimes grew to become obvious weeks or months later when traders tried to withdraw their funds. Some found their accounts have been locked, whereas others have been informed they wanted to pay extra charges or taxes earlier than the criminals may launch their cash.
The criminals then exploited the losses they’d created.
Prosecutors stated recovered server information confirmed the operators contacted victims a number of weeks after the preliminary fraud, claiming they may get well the lacking belongings.
The second strategy allowed the community to make use of data collected in the course of the funding rip-off to focus on individuals already going through substantial monetary losses.
Authorities didn’t disclose what number of victims acquired these restoration presents or whether or not they made extra funds.
The findings mirror a broader sample the FBI has recognized, warning that fraudulent cryptocurrency restoration companies typically goal individuals who have already misplaced funds to funding scams.
Such operations can demand upfront funds, present deceptive asset-tracing stories or falsely declare relationships with regulation enforcement companies to steer victims to ship extra money.
Within the Brooklyn case, investigators targeting dismantling the infrastructure that enabled the prison community to take care of its web sites and repeatedly contact victims.
The District Legal professional’s Digital Foreign money Unit had beforehand seized or disrupted about 400 domains linked to cryptocurrency funding fraud. Nonetheless, substitute web sites appeared rapidly, permitting fraudulent operations to proceed regardless of the enforcement actions.
That prompted investigators to develop their efforts past the web sites themselves.
Throughout an operation spanning three time zones final week, prosecutors executed search warrants and coordinated the disruption of cloud-based servers hosted by firms in Jap Europe and the USA.
The prison community relied on infrastructure and web addresses in Ukraine and different Jap European nations to function, in keeping with the District Legal professional’s Workplace.
By concentrating on the servers, investigators sought to chop off entry to the software program, web site information, and sufferer information the fraudulent platforms wanted to function.
The transfer additionally aimed to forestall the scammers from rapidly rebuilding their web sites and utilizing saved buyer data to strategy present victims with additional restoration presents.
The enforcement effort concerned cooperation from the FBI and several other private-sector organizations, together with Shadowserver, Coeus and UltaHost.
Regardless of the dimensions of the disruption, recovering the stolen cryptocurrency stays a separate problem.
Prosecutors estimate the scheme stole tens of thousands and thousands of {dollars}, however investigators have seized solely about $300,000 in stolen belongings to this point.
The District Legal professional’s Workplace has not disclosed whether or not victims have recovered any of these funds or supplied a timetable for restitution. The announcement additionally didn’t determine the alleged operators or announce arrests.
Investigators proceed efforts to get well extra belongings, leaving many of the cash stolen by the multinational operation unaccounted for.


