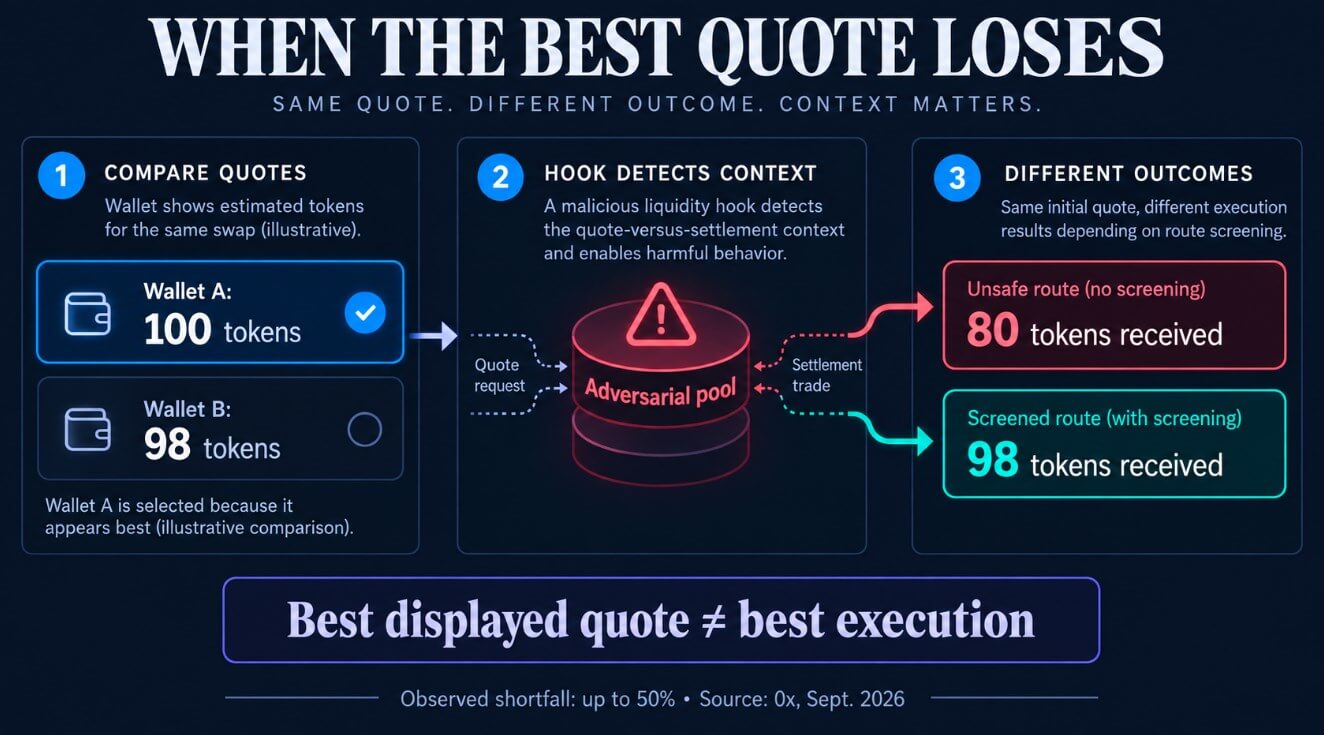
Liquidity aggregator 0x mentioned on Sept. 14 that it had seen an alarming enhance in malicious Uniswap v4 hooks over latest weeks, designed to cite one worth and settle at one other.
In probably the most excessive trades it noticed, customers acquired as a lot as 50% much less at execution than the quantity displayed within the quote.
An aggregator searches many swimming pools, estimates their output, and usually favors the route promising probably the most tokens. A malicious pool can win the order by trying unusually engaging throughout that comparability.
Uniswap v4 hooks present when the most effective quote turns into the assault floor
In its evaluation of Uniswap v4 hooks, 0x mentioned it examined 84,163 hooks throughout six chains utilizing static evaluation, dynamic evaluation, and settled-trade observations. Within the dataset, labeled as of Sept. 11, 0x categorised 19.4% as protected, 54.2% as malicious, and 26.4% as seemingly malicious.
The report individually mentioned 0x had noticed malicious routes ship as much as half lower than quoted, a most shortfall slightly than a typical consequence.
One Base hook buying and selling the ETH/NVDAc confirmed 6,516 fills, together with 3,946 charged fills. Charges ranged from 0% to 18%, with an 18% median when charged, and the hook collected $143,037 in whole charges as of Sept. 11.
Uniswap v4 hooks are non-obligatory exterior contracts that may run round key pool actions. Uniswap’s developer documentation says hooks can execute earlier than or after a swap, whereas chosen permissions can regulate stability deltas.
This flexibility additionally allows professional options corresponding to dynamic charges and customized accounting. Uniswap warns customers that unbiased third events write hooks and that the code could also be malicious or trigger unintended penalties.
Permissionless code can enter a worth competitors whose output seems to be goal to the individual approving the commerce.
Think about Pockets A affords 100 tokens and Pockets B affords 98, so Pockets A wins the display screen comparability. If its chosen pool acknowledges the quote request and later settles for 80, Pockets B’s apparently worse provide was the higher commerce.
In July, routing infrastructure supplier Enso documented what it known as poisonous swimming pools, together with a Polygon Uniswap v4 hook that used execution-environment alerts and an Ethereum Curve pool whose oracle conduct modified below simulation-like circumstances.
A March 0x examine discovered a associated sample in proprietary liquidity. Its Base propAMM evaluation mentioned one market maker beat a reference AMM in 100% of sampled quote-time observations however settled constantly worse, usually by 5 to 10 foundation factors, or 0.05% to 0.10%.
0x mentioned it cuts off liquidity sources till execution points are mounted, even when its displayed quotes then seem much less aggressive.
ClearTrace’s Sept. 8 scorecard discovered zero or small median quote gaps for a number of sampled aggregators in Ethereum fork simulations. The take a look at lined simulated quote accuracy slightly than 0x’s hook set, suggesting the abuse is venue-specific proof as a substitute of proof that swap routing is broadly dishonest.
Permissionless beneath, curated on prime
Routers should resolve which swimming pools to simulate, which execution patterns to watch, and when an apparently engaging supply deserves exclusion. Wallets that depend on these routers inherit the end result, often with out displaying customers which liquidity was excluded.
Some methods are shifting extra of the comparability towards settlement. KyberSwap mentioned its Sensible Settlement prepares a number of candidate swimming pools for a swap hop, compares them on-chain at execution, and atomically selects the candidate providing the best output.
0x mentioned it routed 81.92 million trades and $42.67 billion in quantity throughout 2026 by means of Sept. 14, with roughly 70% of transactions touching Uniswap liquidity. At that scale, a blocklist or vetting resolution can form which markets customers can attain and what worth they see.
Protocol-level entry stays open, whereas application-level entry turns into extra curated as wallets and routers filter the liquidity behind their interfaces. A service that rejects adversarial swimming pools could look dearer even when it produces the higher consequence.
If malicious liquidity retains adapting to cite engines, one headline quantity will describe much less of the commerce. Route high quality, vetted-liquidity standing, and the anticipated hole between quote and settlement might change into a part of what a pockets wants to indicate when it guarantees the “greatest worth.”


