Key Takeaways:
WaterPlum hacked over 30,000 gadgets in 100+ international locations and accessed data from 7,000+ crypto wallets.Pretend jobs, coding checks and malicious code focused crypto, blockchain and Web3 builders.A minimum of $1.8 million in tokens had been despatched to WaterPlum’s wallets by Japanese authorities.
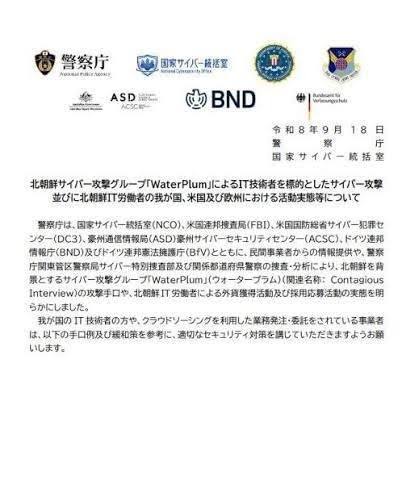
Japan’s Nationwide Police Company (NPA) has uncovered a large-scale cyber marketing campaign concentrating on IT professionals, with cryptocurrency theft on the middle of the operation. The investigation linked the WaterPlum group to exercise related to North Korean IT staff and uncovered infrastructure used to cover their identities and places.

WaterPlum Turns Pretend Jobs Into Crypto Theft
The NPA stated the marketing campaign could be initiated round December 2025 and finish in July 2026. It was thought that greater than 30,000 computer systems in over 100 international locations and areas had been contaminated.
The primary targets included internet builders and designers, in addition to crypto and blockchain consultants. WaterPlum allegedly reached out to victims via social media, recruitment websites, gigs and freelance marketplaces.
The attackers would steadily disguise themselves as trusted crypto, AI or NFT corporations. On-line Interviews had been then adopted, the place candidates needed to resolve software program issues and/or coding assignments.
Some candidates got assignments to obtain information from improvement websites or code repos in lieu of a typical technical project. It’s potential for these information to have malware that may compromise the sufferer’s machine.
Learn Extra: Revolut Crypto Knowledge Leak Exposes Bitcoin Information, Attackers Demand Cost to Cease Extra

Malware Went After Pockets Credentials
The NPA discovered a number of malware households related to the assault: OtterCandy, OtterCookie, InvisibleFerret, BeaverTail and StoatWaffle.
If a system will get contaminated with the malware, it could possibly grant persistent entry within the system, and extract delicate data from it. The catcher may seize browser cookies, clipboards, keystrokes, screenshots and information saved on the pc.
The most important threats confronted by crypto customers had been pockets credentials. Based on the NPA, over 7,000 cryptocurrency pockets data had been stolen. Personal keys and seed phrases had been among the many data sought by the attackers.
The investigation additionally uncovered a minimal of ¥1.7 billion ($10.71 million RTW) of cryptocurrency moved to wallets operated by WaterPlum. That is an estimate of funds which were recognized by investigators, not an estimate of all potential losses.
North Korean IT Employees Add a Second Crypto Danger
The investigation additionally discovered one other solution to generate profits with Tech jobs. Japanese officers found and blocked a brand new “laptop computer farm” the place computer systems had been saved by a facilitator, and managed remotely by North Koreans. Such machines may then be employed by staff to just accept jobs and look like coming from Japan.
A minority additionally used stolen or mis-used identification papers and using VPS to masks the precise identities of the employees. Crypto and different belongings valued at over tons of of hundreds of thousands of yen have been despatched overseas in incidents linked to the investigation, investigators stated.
The NPA and the FBI concluded that the actions of WaterPlum and a few North Korean IT staff had been being directed by the Munitions Trade Division’s Bureau 313 of the Employees’ Social gathering of Korea.
Learn Extra: BonkDAO Hit by $20M Treasury Hack After Malicious Governance Proposal Rocks BONK Holders


