Bitcoin enchancment proposal BIP461 might make a hidden route for leaking pockets secrets and techniques simpler to detect. The draft defines a typical signing process for ECDSA, an present Bitcoin signature scheme.
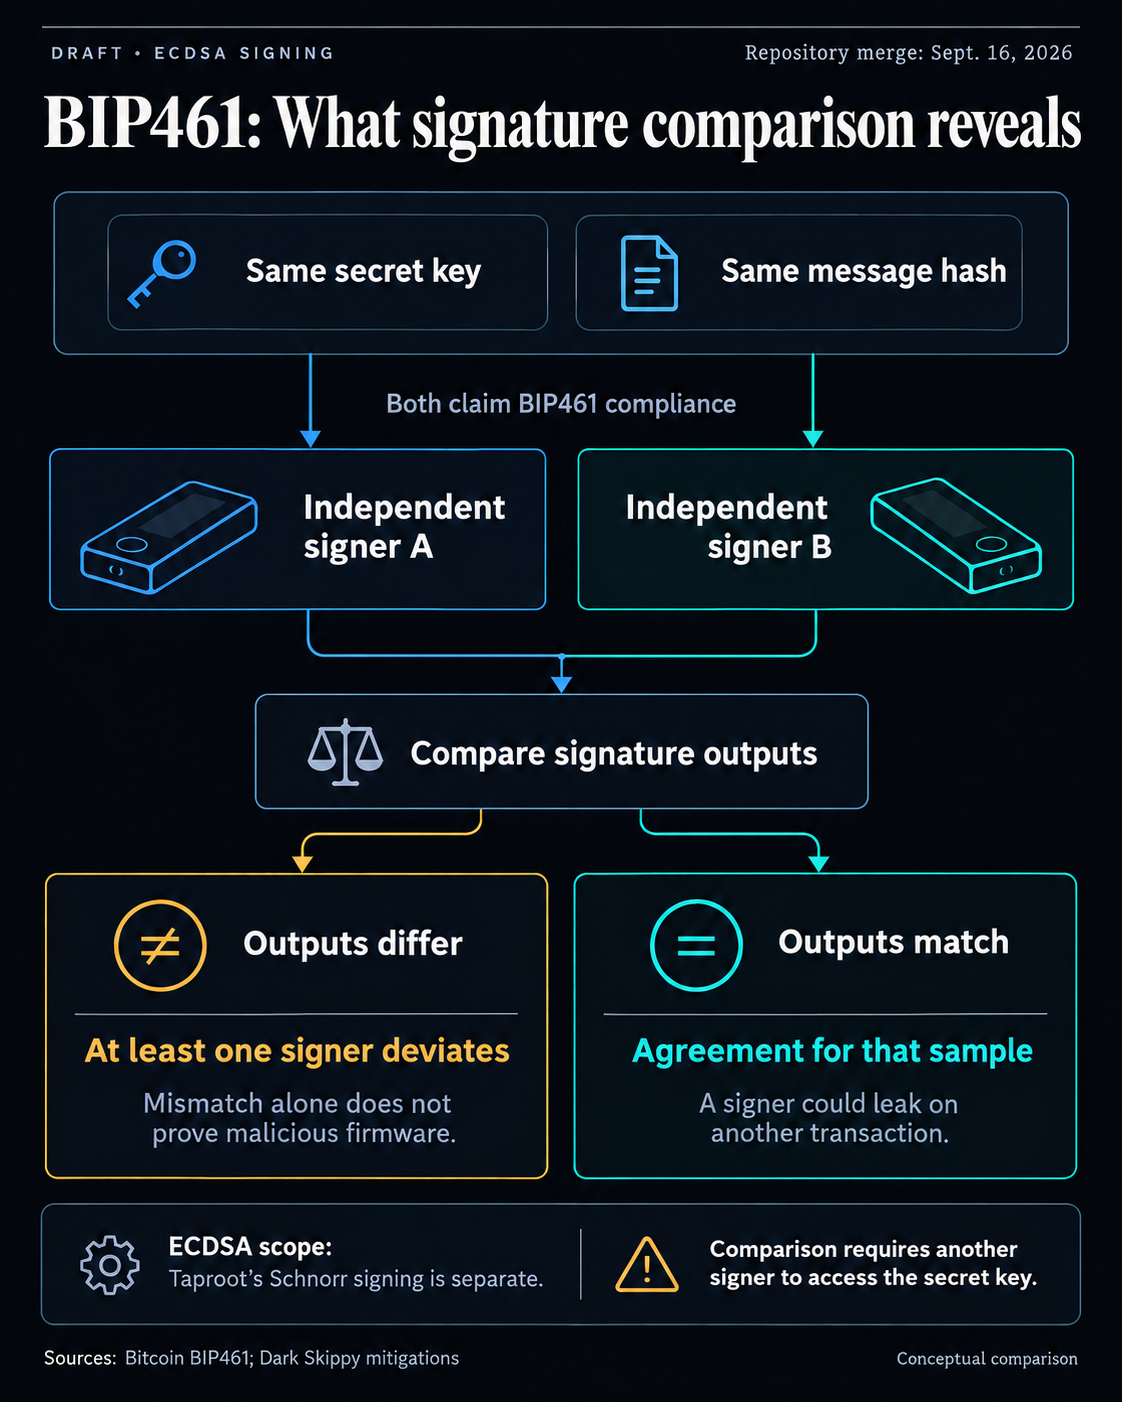
Impartial compliant signers ought to produce equivalent signatures for a similar secret key and message hash, making a benchmark for detecting departures that might conceal key leakage.
Authored by Liam Gilligan, the proposal was merged into the BIPs repository on Sept. 16 and stays marked Draft. Its signatures work underneath present Bitcoin consensus guidelines, so implementing this signing process requires no consensus change.
Evaluating signatures for deviations
ECDSA permits a signer selections whereas creating a sound signature, together with the nonce, a brief worth utilized in signing. Malicious firmware can exploit that freedom to cover key materials in signatures that also go verification, and BIP461 fixes these selections via a specified deterministic process.
Bitcoin’s acceptance of a signature can’t set up that its creation saved the important thing secure. A standard specification provides an anticipated output in opposition to which the signer’s habits could be checked.
The comparability requires equivalent inputs and the very same customary, together with entry to the key key on one other impartial signer. That additional publicity is a sensible price of reproducing the signature. Totally different outcomes for a similar key and message hash present that at the very least one signer is just not following BIP461.
An sincere implementation utilizing one other legitimate ECDSA process can even disagree. A mismatch warrants investigation into compliance, however its trigger stays unresolved. The comparability alone can’t determine a malicious system or show theft.
The prescribed algorithm additionally retains signatures to at most 70 bytes in the usual DER encoding, excluding Bitcoin’s one-byte sighash flag.
The Darkish Skippy disclosure identified that corrupted firmware can embed seed materials in transaction signatures. Of their authentic disclosure, the researchers mentioned that they had not seen the method within the wild.
Darkish Skippy’s authentic demonstration makes use of Schnorr signing, whereas BIP461 specifies ECDSA. Taproot makes use of the separate BIP340 Schnorr scheme, so this draft doesn’t immediately standardize a treatment for that demonstration.
The researchers’ mitigation dialogue warned {that a} malicious signer might leak solely on a particular transaction, so a tool might produce compliant signatures in a check and leak on one other transaction.
On the September merge, a reviewer mentioned check vectors and a reference implementation have been wanted for BIP461 to advance to Full.
For pockets customers, its potential worth is a shared benchmark that might make deviations seen. Delivering that worth nonetheless relies on compliant implementations and comparisons that account for each detection limits and the dangers of dealing with secrets and techniques.


