An electronic mail handle hosted on an actual authorities area triggered Revolut to switch buyer KYC information and monetary information to a pretend requester. The London-based fintech confirmed the incident on September 12, stating that the fraudulent requests have been processed as a result of the emails carried legitimate area authentication info and have been believed to be official communications.
Revolut stated the incident affected a “very restricted” variety of its greater than 80 million particular person prospects, whereas person methods and funds weren’t impacted. The corporate has not but disclosed the precise variety of individuals, the markets concerned, the company whose area was used, or how lengthy the incident lasted.
How a Pretend Authorities Request Bought By means of
Based on a buyer notification posted on Telegram by blockchain investigator ZachXBT, a minimum of one request got here from an unauthorized electronic mail account. Nonetheless, it was despatched straight via the official area of a authorities company.
The e-mail carried legitimate area authentication info, main Revolut to imagine the request got here from a licensed authority and proceed to offer the information. The corporate described the incident to TechCrunch as a “refined exterior impersonation assault.”
This was not a website spoofing try utilizing a website identify spelled equally to the official handle. Area authentication signifies the e-mail was despatched via infrastructure permitted by the area, nevertheless it doesn’t verify whether or not the particular person behind the account has authority to request information or whether or not the request has a legitimate authorized foundation.
Revolut has not disclosed how the third celebration obtained the suitable to ship emails via the federal government area, what accompanying paperwork got here with the request, or whether or not the corporate carried out extra verification steps earlier than responding.
KYC Information and Bitcoin Information Had been Disclosed
Based on the notification despatched to prospects reviewed by TechCrunch, the information supplied included full names, dates of beginning, dwelling addresses, emails, cellphone numbers, and copies of identification paperwork similar to passports or driver’s licenses. Verification selfies used for KYC identification checks, financial institution statements, IBANs, withdrawal histories, and full transaction histories may fall inside the affected scope.
The notification shared by ZachXBT reveals that this transaction historical past consists of Bitcoin as nicely. Revolut additionally said that facial biometric information was not affected, though the unique selfie photograph could have been supplied.
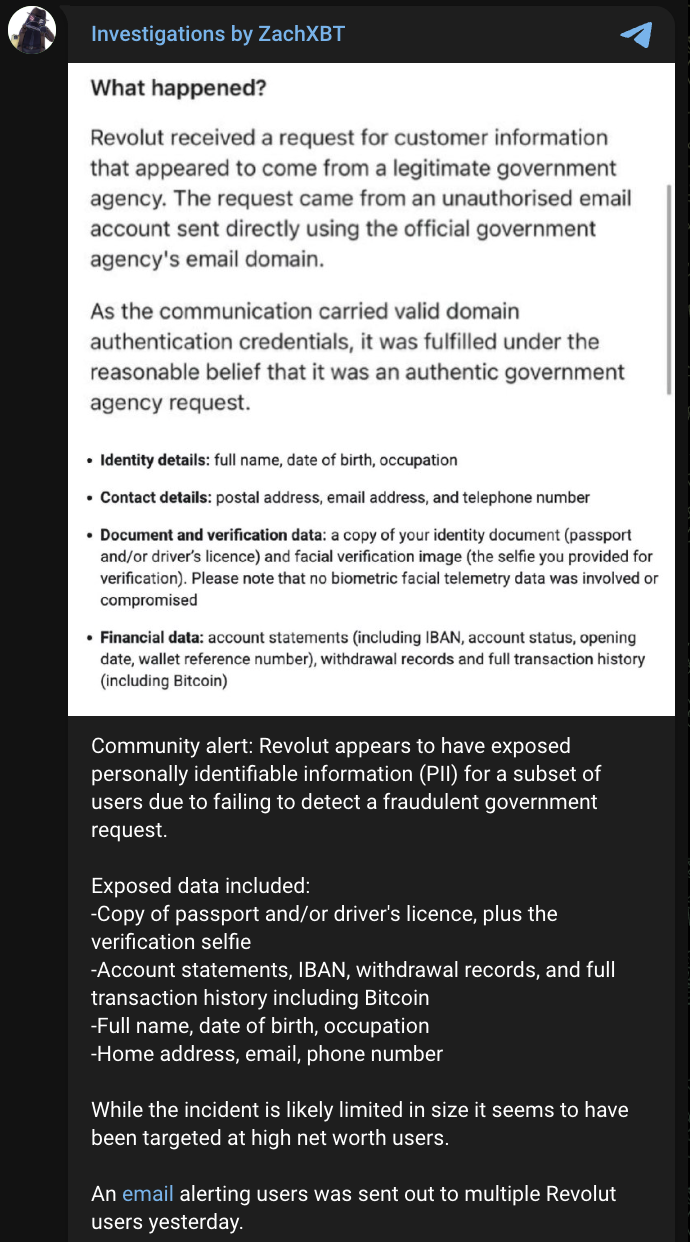
Revolut notification shared by ZachXBT. Supply: Telegram.
The supplied information may improve the chance of impersonation, identification theft, and focused fraud. KYC info mixed with Bitcoin transaction historical past may make phishing calls or messages extra convincing.
ZachXBT believes the incident was small in scale however appeared to focus on high-net-worth customers. Revolut has not confirmed this evaluation.
Revolut Says Funds and Programs Had been Unaffected
Revolut said that inside methods weren’t compromised and buyer funds weren’t affected. Knowledge was exfiltrated in the course of the processing of the pretend request, quite than being taken via direct entry to person accounts.
After discovering that the sender was unauthorized, Revolut blocked the e-mail handle and alerted the federal government company whose area was used. The corporate additionally contacted affected prospects whereas notifying regulation enforcement, information safety authorities, and monetary regulators.
Revolut has not clarified when the request was obtained, when the information was transferred, or how lengthy it took to detect the incident. Underneath UK GDPR, guided by the ICO, a breach more likely to end in a threat have to be reported to the supervisory authority inside 72 hours of the group changing into conscious of it. Revolut stated it has notified the related events however has not specified when this was executed.
The Safety Hole Past Revolut
The Revolut incident shares similarities with a tactic warned about by the FBI in November 2024, through which criminals used compromised US and overseas authorities emails to ship pretend emergency information requests to companies. The FBI famous listings promoting entry to authorities emails and faux request providers on legal boards in 2023 and 2024, with elevated exercise round August 2024.
The company recommends that companies confirm the sender’s identification, overview accompanying documentation, and make sure the request via an unbiased channel. Revolut has not indicated whether or not it has modified its verification course of or added approval steps for information requests following the incident.


